by Kavio Labs · for WooCommerce 10.1+ on WordPress 6.7+
Stop AI crawlers, scrapers, card testers, vulnerability scanners and unwanted countries before WordPress builds a page. Googlebot and Bingbot are verified by DNS and always allowed; 50+ bots get one switch each; country rules use free GeoIP databases and can close only the checkout (block and classic checkout, wc-ajax and Store API); card testing protection on order submissions; the add to cart flood fix for requests without a WooCommerce session; IP and network lists, rate limits for search, filters, forms and login, honeypots; a one-second challenge instead of a captcha; learning mode, dashboard, log, IP tester and Cloudflare export. HPOS and blocks compatible.
On saleVersion 1.0.0Compatible with WooCommerce 10.1 – 11.2, WordPress 6.7+ No core file edits
Built forWooCommerce
AI crawlers, scrapers, scanners and blocked countries stopped before the page; Googlebot always passes1 of 9
Stop AI crawlers, scrapers, card testers, vulnerability scanners and unwanted countries before WordPress builds a page. Googlebot and Bingbot are verified by DNS and always allowed; 50+ bots get one switch each; country rules use free GeoIP databases and can close only the checkout (block and classic checkout, wc-ajax and Store API); card testing protection on order submissions; the add to cart flood fix for requests without a WooCommerce session; IP and network lists, rate limits for search, filters, forms and login, honeypots; a one-second challenge instead of a captcha; learning mode, dashboard, log, IP tester and Cloudflare export. HPOS and blocks compatible.
WooCommerce 10.1 - 11.2, WordPress 6.7+
Overview
Stop AI crawlers, scrapers, vulnerability scanners, card testers and unwanted countries before WordPress builds a page. Every storefront request is checked right after WordPress loads the plugins, before the theme, the main query and the page exist, from a compiled rule file, so a normal visitor costs no extra database query and a blocked bot never reaches the page code. Googlebot and Bingbot are verified by DNS and always allowed, so your search rankings are safe.
It starts in learning mode: rules only write "would block" entries to the log, so you see what would happen before anything is blocked.
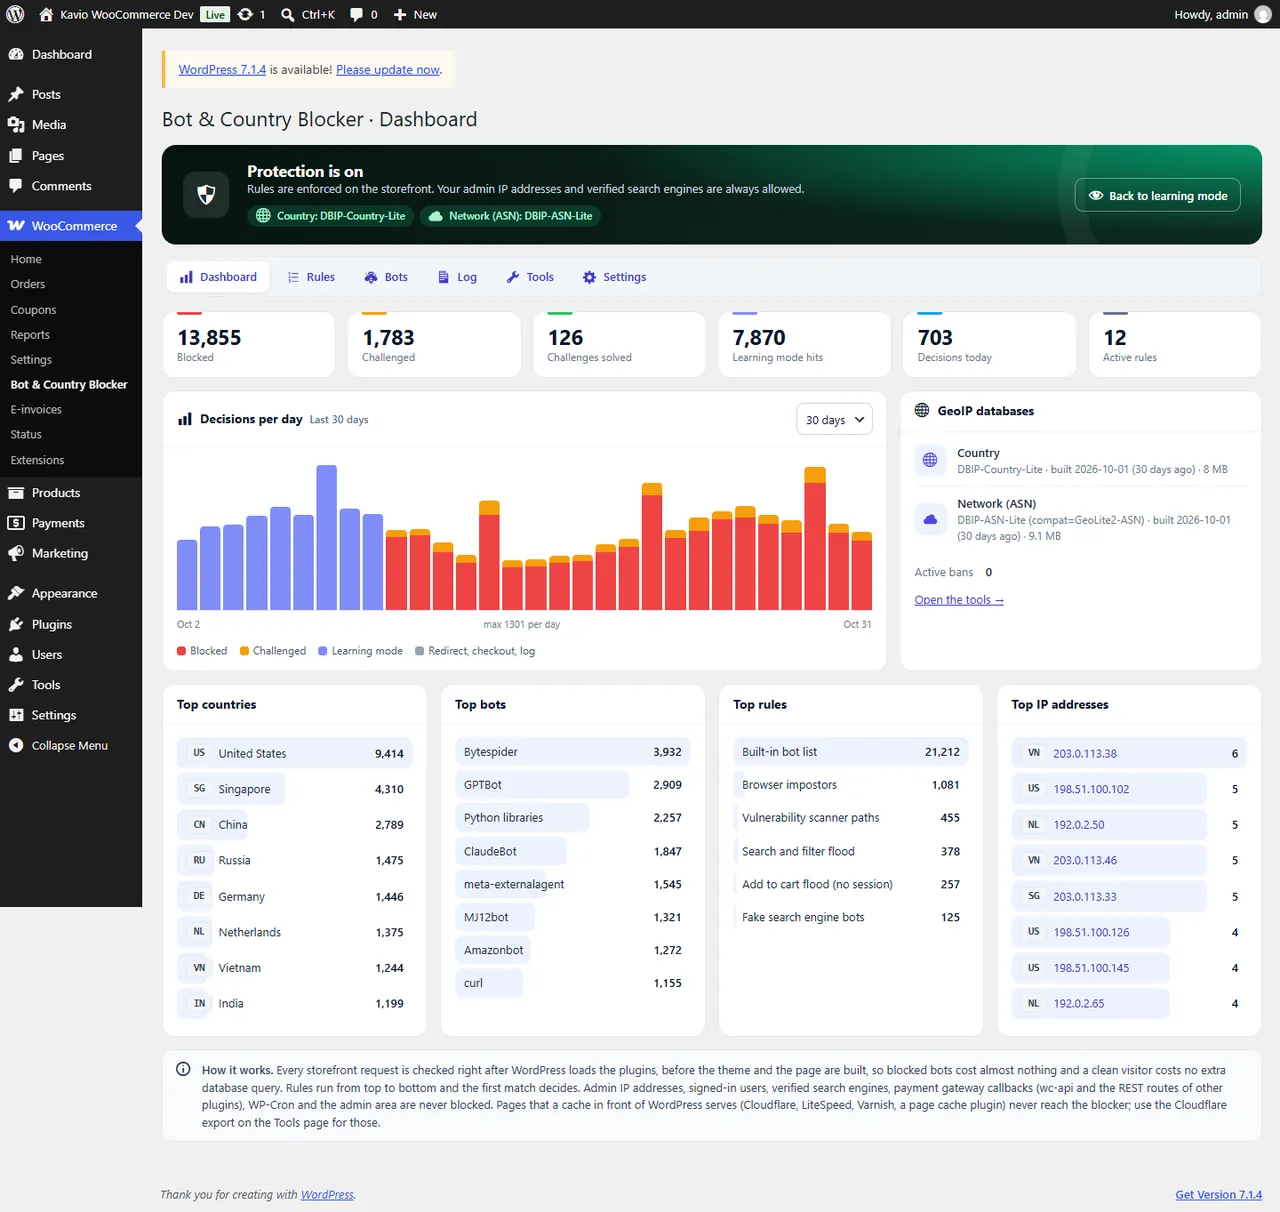
Dashboard with blocked and challenged requests, top countries and bots
Key features
Countries: block, challenge, redirect or close only the checkout for selected countries, or for every country except the selected ones. Free DB-IP Lite country and network databases in one click (no account), MaxMind GeoLite2 with a free key, or upload your own .mmdb; Cloudflare's CF-IPCountry header is used when the request comes through Cloudflare. IPv4 and IPv6.
Checkout only, everywhere: the block checkout, the classic checkout, "pay for order", the classic order submission (wc-ajax=checkout) and the Store API checkout (/wp-json/wc/store/v1/checkout) are all closed for the countries you choose; browsing and the cart stay open.
Card testing protection: bots that try stolen card numbers through your checkout are blocked after 8 order attempts in 15 minutes and banned for an hour (classic, block and "pay for order" checkout).
Add to cart floods: ?add-to-cart= links, wc-ajax=add_to_cart and Store API cart calls from scripts that have no WooCommerce session and do not come from a page of your store get a one-second check, so they stop creating thousands of sessions.
IP addresses and networks: single IPs, CIDR ranges, ranges, IPv6, public list URLs refreshed daily, AS numbers and a preset of 50+ hosting, cloud and server providers.
Built-in bot list with one switch per bot: 50+ AI training crawlers (GPTBot, ClaudeBot, CCBot, Bytespider, meta-externalagent, Amazonbot and more), AI assistants and AI search, SEO crawlers, scripts and HTTP libraries, headless browsers and vulnerability scanners.
Search engines stay safe: Googlebot, Bingbot, Applebot, YandexBot and Baiduspider are verified by reverse and forward DNS and allowed before any rule runs; impostors are blocked.
Rate limits per IP address for the whole store, for product search and filters, and for registration, login, lost password, wp-login.php, xmlrpc.php and comments, with an optional temporary ban.
Honeypot paths (/.env, /.git/, /phpmyadmin/ and more) that ban scanners, empty user agents and browser impostors.
Actions per rule: block (styled, editable 403 page), challenge (a one-second JavaScript proof of work: no captcha, no third-party service), redirect, checkout only, allow, log only. AJAX and Store API calls get a JSON answer.
Dashboard, log and CSV export, IP tester with a decision trace, Cloudflare WAF expressions, AI crawler group for robots.txt, bans and administrator IP addresses.
You cannot lock yourself out: administrator IP addresses are allowed automatically, signed-in users are never blocked (option), the admin area, admin-ajax, WP-Cron, payment gateway callbacks (wc-api) and the REST routes of other plugins are never checked, and an emergency file switches everything off.
Cache safe: block and challenge answers are sent with Cache-Control: no-store and X-LiteSpeed-Cache-Control: no-cache; clean pages are left untouched (no cookie, no header).
Clean install: HPOS and Cart/Checkout blocks compatible, no core or theme file changes, everything removed on uninstall.
Compatibility
WordPress 6.7+, WooCommerce 10.1+ (tested with WordPress 7.1.3 and WooCommerce 11.2.1), PHP 7.4 – 8.3. APCu is used for rate limits when the server has it.
Block and classic themes, block and classic Cart and Checkout, HPOS and the legacy order storage. Multisite: one set of rules per site.
Installation
Requirements
WordPress 6.7 or later, WooCommerce 10.1 or later (tested with 11.2.1), PHP 7.4 – 8.3
Outbound HTTPS from the server for the GeoIP and list downloads (WordPress HTTP API)
About 20 MB free in wp-content/uploads for the GeoIP databases
Install
Download kv-bot-country-blocker-kv.zip from My licences > Downloads on woocommerce.kaviolabs.com.
In WordPress: Plugins > Add New > Upload Plugin, choose the zip, Install Now, Activate.
Open WooCommerce > Bot & Country Blocker. On the dashboard click Download now to install the free DB-IP Lite country and network databases. Skip it if you only use bot rules, or if your store is behind Cloudflare.
Enter your licence key under WooCommerce > Settings > Bot & Country Blocker (the Settings tab of the plugin links there). The plugin works for 14 days without a key.
The daily maintenance (log retention, list URLs, monthly GeoIP update) runs through WP-Cron. If WP-Cron is switched off on your site (DISABLE_WP_CRON), add the cron URL from Tools > Maintenance to your hosting's cron jobs once a day, for example wget -q -O /dev/null "<cron URL>".
After installing
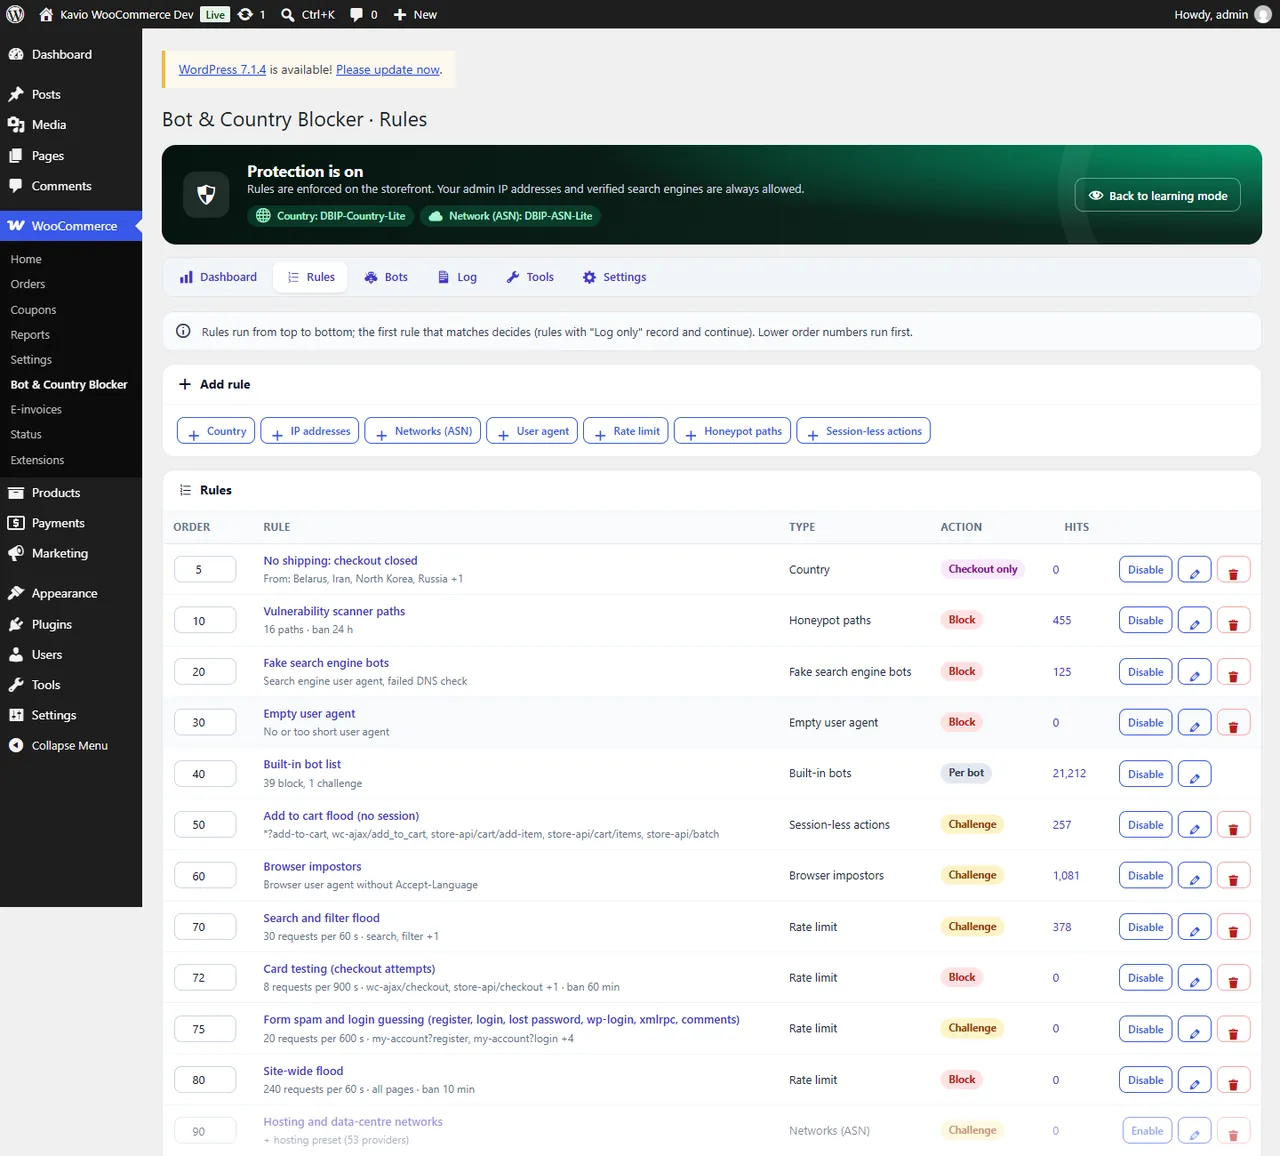
The plugin starts in learning mode with eleven ready-made rules: scanner paths, fake search engine bots, empty user agents, the built-in bot list, the add to cart flood fix, browser impostors, four rate limits (search and filters, card testing, forms and login, whole store) and a disabled hosting-network rule. Look at the Log for a few days, adjust the rules, then click Switch protection on in the header.
Users need the manage_woocommerce capability (Shop managers and administrators) to see and change the pages.
Where the data lives
Seven tables wp_kv_bcb_* (rules, bans, administrator IP addresses, DNS cache, rate buckets, log, daily counters) and the option kv_bcb_config.
The compiled rule file and the GeoIP databases in wp-content/uploads/kv-bot-country-blocker/ (with index.php and a "deny all" .htaccess; on nginx add location ~* /uploads/kv-bot-country-blocker/ { deny all; }). The rule file itself is a PHP file that exits when opened.
Updating
Upload the new zip the same way (WordPress offers to replace the installed version). Rules, settings, the log and the databases are kept.
Uninstalling
Plugins > Deactivate, then Delete removes the seven tables, the settings, the compiled rule file, the downloaded databases, the scheduled event and its group from a physical robots.txt. Orders and customers are never touched.
Configuration
Open WooCommerce > Bot & Country Blocker. The header shows the mode (learning or protection) and the GeoIP databases; the tabs are Dashboard, Rules, Bots, Log, Tools and Settings. The licence key is entered under WooCommerce > Settings > Bot & Country Blocker.
Rules in the order they run
Rules
Rules run from top to bottom; the first rule that matches decides. "Log only" rules record and continue. Change the order numbers and click Save order. Add a rule with the buttons at the top:
Type
Matches
Notes
Country
the visitor's country, in or not in the list
needs the country database or Cloudflare; unknown countries never match
IP addresses
IPs, CIDR, ranges, IPv6, plus an optional public list URL
the list is downloaded daily; plain text, CSV and JSON work
Networks (ASN)
AS numbers, optional hosting preset (50+ cloud and server providers)
needs the ASN database
User agent
text (case-insensitive) or /regular expressions/
Rate limit
more than N requests per S seconds per IP, on all pages or listed routes
optional ban in minutes
Honeypot paths
URLs only scanners ask for
bans the IP for the given hours
Session-less actions
add to cart calls without a WooCommerce session that do not come from a page of the store
?add-to-cart=, wc-ajax=add_to_cart, Store API cart
The built-in rules Fake search engine bots, Empty user agent, Browser impostors and Built-in bot list exist once: switch them on or off and choose their action.
Routes name what a request does: search (?s=), filter (layered navigation and price filters), checkout, checkout/order-pay, cart, my-account (and its endpoints, such as my-account/lost-password), wp-login, xmlrpc, comment, wc-ajax/<action> (for example wc-ajax/checkout), store-api/<path> (for example store-api/cart/add-item; store-api/checkout is the order placement of the block checkout) and page for everything else. store-api/cart/* matches every route below store-api/cart/; my-account?register matches only when the register field is posted; *?add-to-cart matches any page with the add-to-cart parameter.
Actions
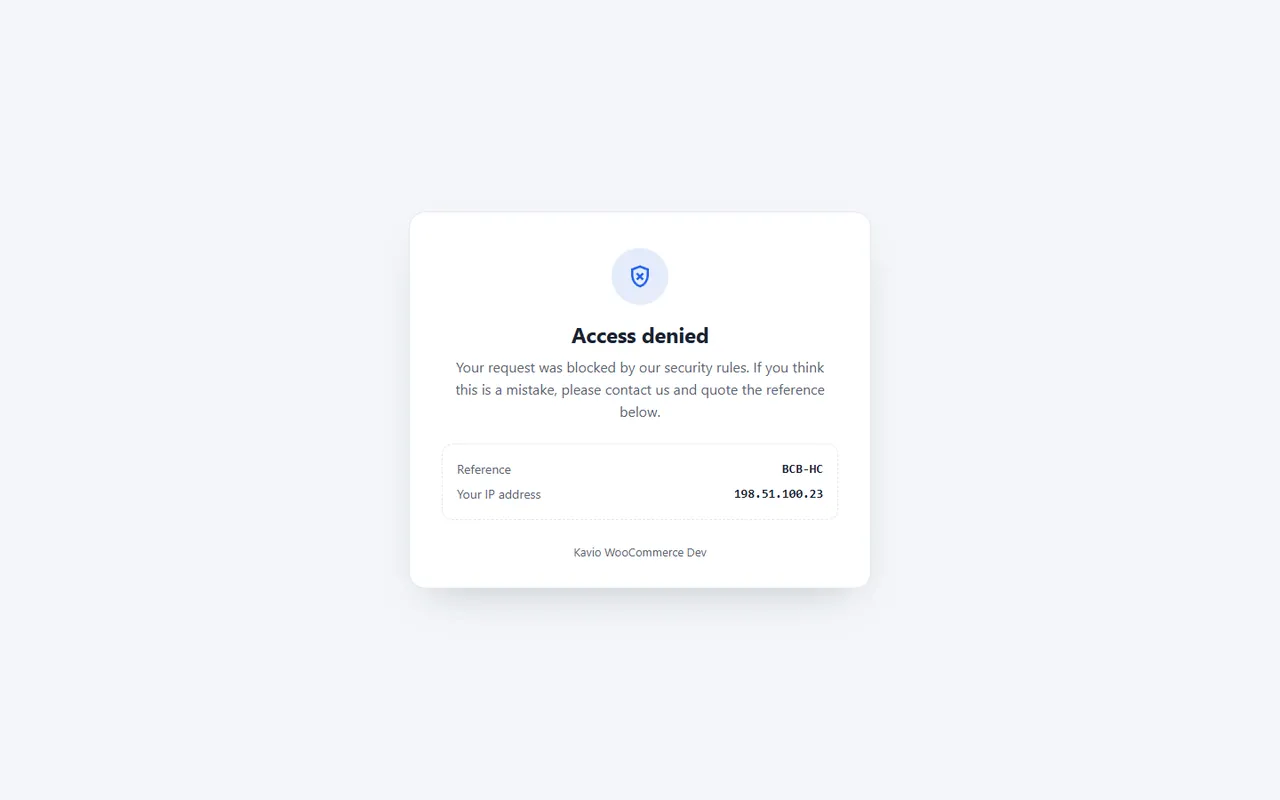
Block: the block page (HTTP 403) with a reference such as BCB-4F2K.
Challenge: a browser check that takes about a second (proof of work, no captcha, no third-party service). People pass once and are not asked again for the configured hours; scripts cannot pass.
Redirect: to a URL or a path.
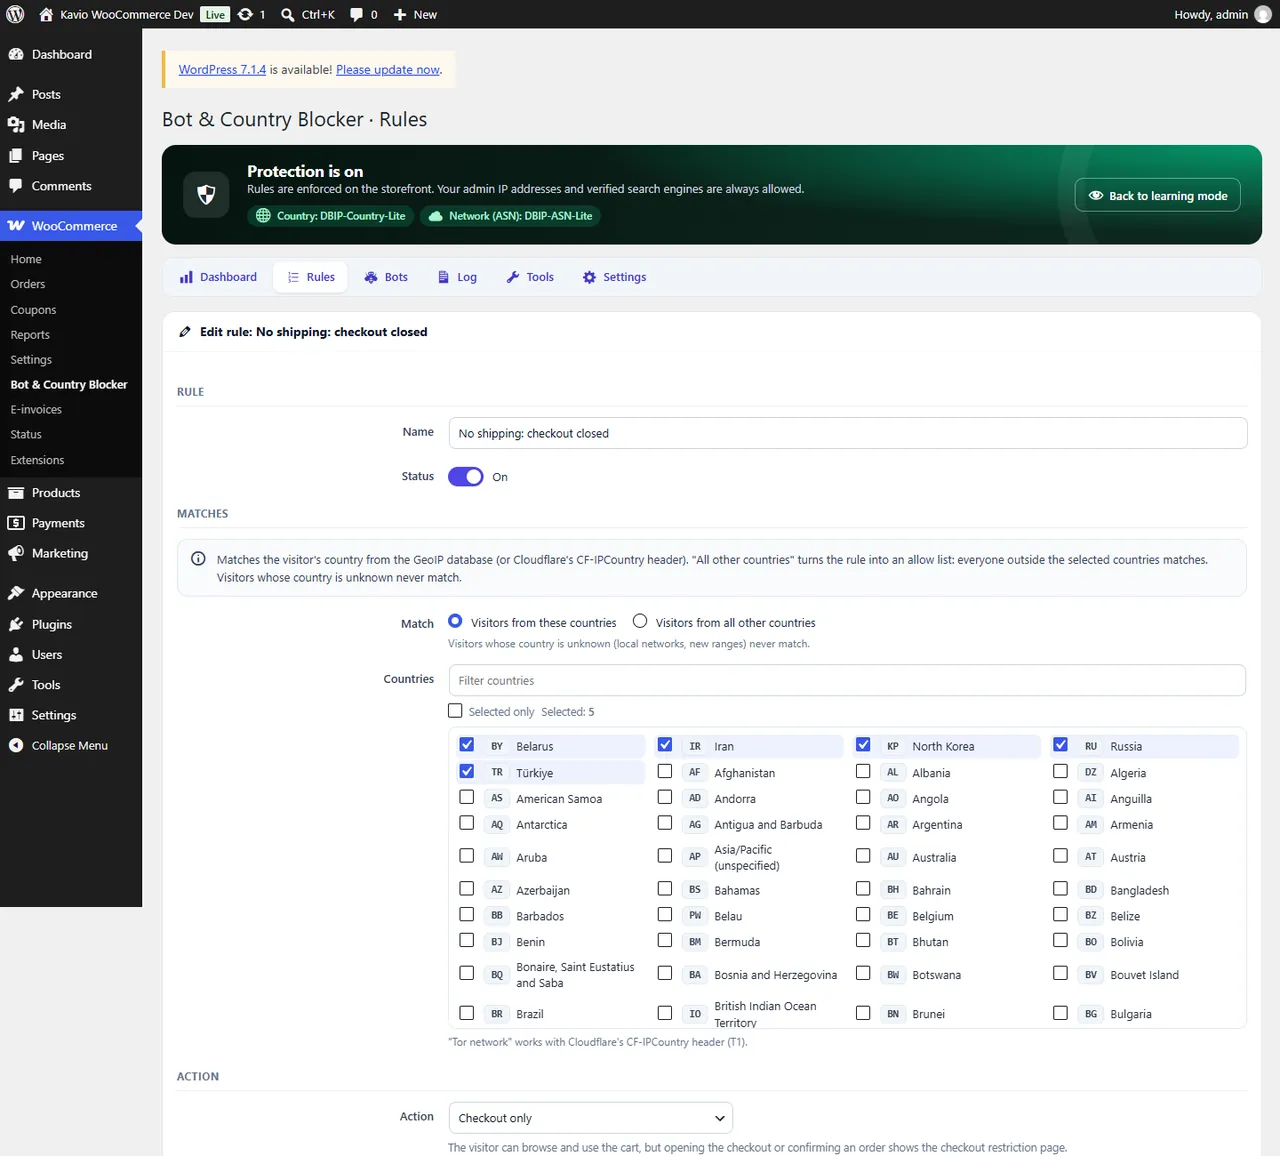
Checkout only: the visitor can browse and use the cart; the checkout page (block and classic), "pay for order", the classic order submission and the Store API checkout show the checkout restriction page (or a JSON 403 for the API calls). The "order received" page stays open. Use it for countries you cannot ship to.
Allow: skips all later rules (put it on top for your office or partners).
Log only: records and continues.
Country rule with the checkout-only action
Bots
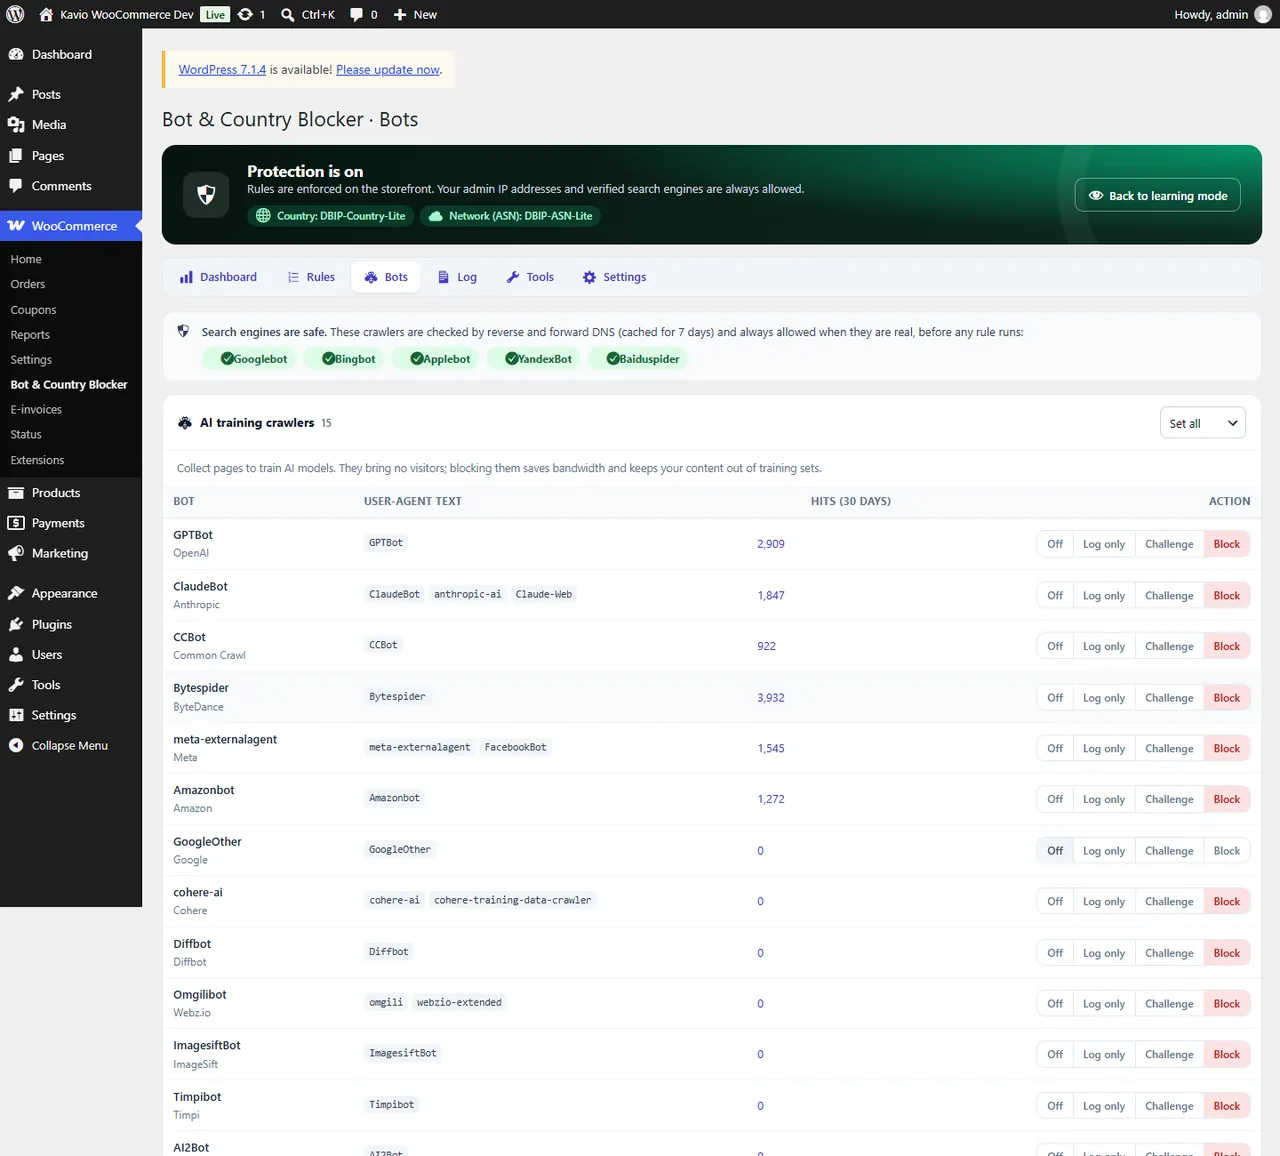
One switch per bot: Off, Log only, Challenge or Block, and Set all per group. AI assistants (ChatGPT-User, OAI-SearchBot, PerplexityBot and others) are off by default because they fetch pages when a person asks about your products; AI training crawlers are blocked by default. Googlebot, Bingbot, Applebot, YandexBot and Baiduspider are not in the list: they are verified by DNS and always allowed when real.
One switch per bot
Settings
Status and Learning mode.
Never blocked: signed-in customers, verified search engines, administrator IP addresses (remembered for N days), and your own paths or routes (for example a product feed).
Block and challenge pages: accent colour, titles and messages (placeholders [store], [ip], [country], [ref]), challenge difficulty, how long a solved challenge is valid.
IP address and GeoIP: Automatic trusts Cloudflare's CF-Connecting-IP only from Cloudflare edge addresses and your proxy header only from the trusted proxies you list; otherwise the connection address is used, which cannot be forged. Monthly GeoIP update (DB-IP Lite or MaxMind GeoLite2) and the MaxMind account ID and licence key.
Log: retention in days and maximum rows.
License (own-site edition): your license key and its status.
Card testing is a rate limit on order submissions (wc-ajax/checkout, store-api/checkout, checkout/order-pay?woocommerce_pay): 8 attempts per IP address in 15 minutes, then the address is blocked and banned for 60 minutes. Change the numbers on the rule if your shop has many orders from one office address.
Usage
First week: learning mode
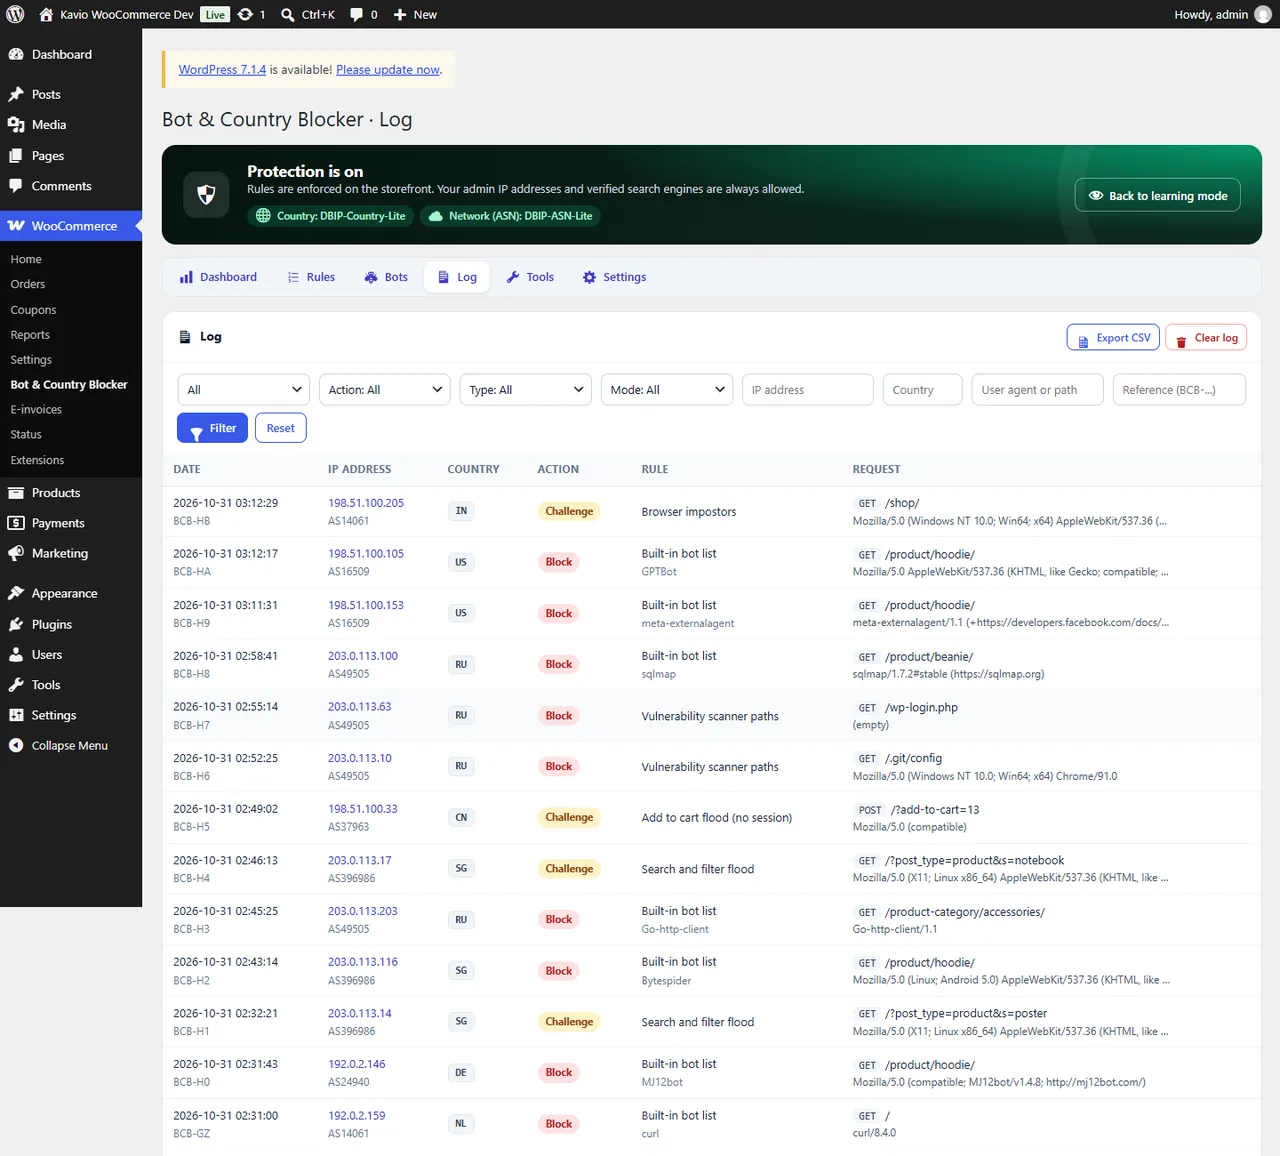
After installing, every rule only logs. Open the Log and filter by rule or action; look for real customers among the "would block" entries. Typical adjustments: switch off a rate limit for a busy business customer, allow an integration's user agent, or set an SEO tool you use to Off on the Bots page. Then click Switch protection on.
The log with filters and CSV export
Dashboard
Blocked and challenged requests, solved challenges, learning-mode hits and today's decisions; a 7, 30 or 90 day chart; top countries, bots, rules and IP addresses. Click an IP address to see its log entries.
When a customer says "I am blocked"
Ask for the reference on the block page (for example BCB-4F2K) and type it in the log filter: you see the rule, the IP address, the country and the user agent. Add an Allow rule for the address on top, or change the rule.
Tools
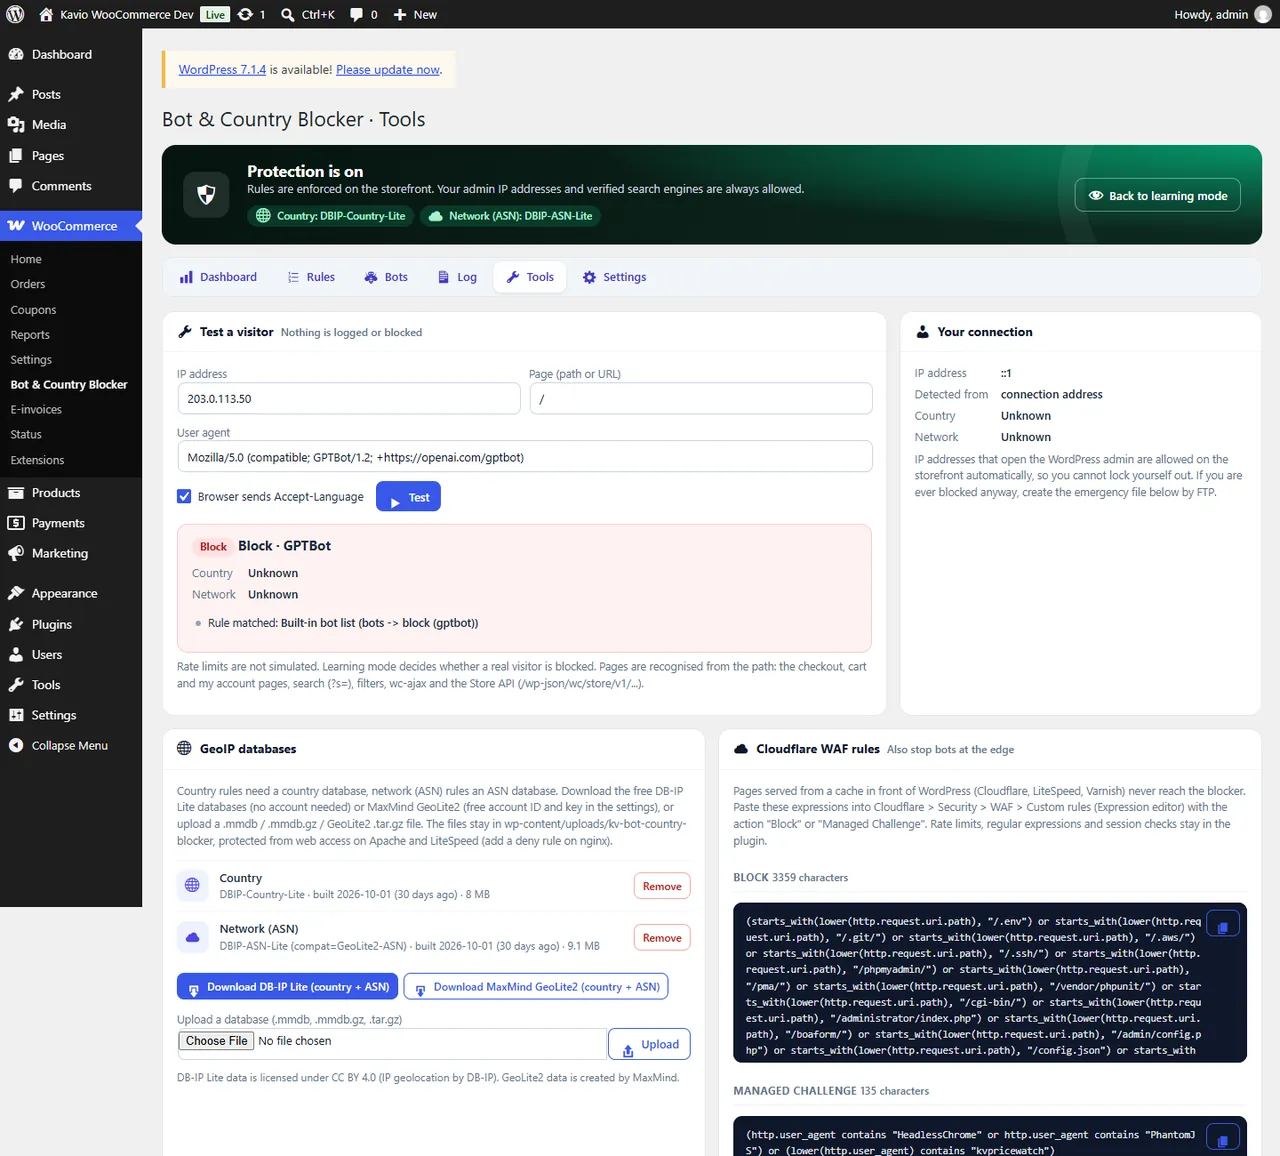
Test a visitor: enter an IP address, a user agent and a page (/index.php?controller=search or a friendly URL); the result shows the country, the network and every step of the decision. Nothing is logged or blocked.
GeoIP databases: download DB-IP Lite or MaxMind GeoLite2, upload a file, remove a database.
Cloudflare WAF rules: expressions for "Block" and "Managed Challenge" built from your rules, to stop the same bots at the edge, in front of cached pages.
AI crawlers in robots.txt: add or remove a Disallow: / group for the AI crawlers you block. Without a physical robots.txt the group is added to the virtual robots.txt of WordPress; with a robots.txt file in the site root the file is edited (a backup is kept as robots.txt.kv-backup).
Maintenance: last run, run now, the cron URL. Active bans and administrator IP addresses can be removed here.
Tester, GeoIP databases and Cloudflare export
The pages visitors see
Self-contained pages in your accent colour, light and dark, readable on phones, never cached and marked noindex.
Block page
Block page: title, message, reference and IP address (optional).
Challenge page: a progress bar; passes on its own in about a second and returns to the page the visitor asked for.
Checkout restriction page: message, detected country and a "Back to the store" button.
AJAX calls (add to cart and similar) get a JSON answer with status 403 instead of a page.
Emergency switch
If you ever lock yourself out of the storefront, create an empty file wp-content/kv-bot-country-blocker.off (FTP or file manager), or add define( 'KV_BCB_DISABLED', true ); to wp-config.php. The blocker stops at once; delete the file to turn it back on. The WordPress admin is never blocked.
FAQ
Will it hurt my Google rankings?
No. Googlebot, Bingbot, Applebot, YandexBot and Baiduspider are verified by reverse and forward DNS (cached for 7 days) and allowed before any rule runs, even before country or rate-limit rules. Fake crawlers that only copy Googlebot's user agent are blocked.
Do I need Cloudflare or a paid GeoIP service?
No. Country and network data come from the free DB-IP Lite databases (no account, CC BY 4.0) or MaxMind GeoLite2 (free account). Both are files on your server, read by the plugin itself. If your store is behind Cloudflare, its country header is used as well.
How fast is it?
The rules are compiled into one small file read once per request; a clean visitor costs no database query. Country lookups read a few bytes of the database file. Only blocked, challenged or logged requests write a log row.
Does it work with page caches?
Block, challenge and checkout answers are sent with Cache-Control: no-store and X-LiteSpeed-Cache-Control: no-cache, so a cache never stores them, and clean pages get no cookie and no header from the plugin. Pages that a cache in front of WordPress serves (Cloudflare, LiteSpeed, Varnish, a page cache plugin) never reach PHP: use the Cloudflare export for the edge.
Does it stop fake registrations and contact form spam?
Most spam comes from scripts, hosting networks and a few countries. The bot list, the hosting preset, browser impostors, the form and login rate limit (registration, login, lost password, wp-login.php, xmlrpc.php, comments) and country rules stop them before the form is shown. Keep a captcha plugin if you want a second layer.
Can I close only the checkout for some countries?
Yes: a Country rule with the action Checkout only. Visitors can browse and use the cart; the checkout page, "pay for order", the classic order submission and the Store API checkout show the restriction page. It works with the block and the classic checkout.
What about my payment gateway, other plugins and cron?
Payment gateway callbacks (wc-api), the REST routes of other plugins (webhooks of Stripe, PayPal and others), authenticated REST API clients, admin-ajax, WP-Cron and the admin area are never checked. Add your own integrations (feeds, other cron URLs) to the exempt paths in the settings.
Does it stop card testing?
Yes. Order submissions are limited to 8 per IP address in 15 minutes (classic checkout, block checkout through the Store API, "pay for order"); after that the address is blocked and banned for an hour. Country, network and bot rules apply to the checkout as well.
What happens when the license is not active? (own-site edition) After the 14-day start period without a key, rules only log, as in learning mode. The dashboard, rules, log and tools keep working. The CodeCanyon edition never locks features (the purchase code is for updates and support).
Which data is stored?
For blocked, challenged or logged requests: time, IP address, country, network, user agent, method, path and the rule. Entries are deleted after the retention period (30 days by default). Clean visitors are not logged.
The department store block theme for WooCommerce: colour-coded departments, a department list beside the hero slider with two side promos, a big search with a department picker, tabbed product grids, a 2 + 1 + 2 offer grid, deals of the day with real countdowns, a department showcase, a promotions band and a three-column product page with a sticky buy box. Four styles (Meridian, Harbor, Citrus, Night) as Site Editor style variations, every colour editable. Cart and Checkout blocks styled, HPOS neutral.
Flagship multipurpose block theme: five ready-made stores (Fashion, Electronics, Home, Beauty, Grocery) imported with one click, each switching colours, fonts, header, footer and home page. Three headers, two footers, mega menu, quick view, wishlist and compare, live search, AJAX filters, colour and size swatches, deal countdowns, a sticky add-to-cart bar and a free-shipping bar.